HIPAA Professional Training
Formal training in HIPAA Privacy Rule, Security Rule, and Breach Notification standards.
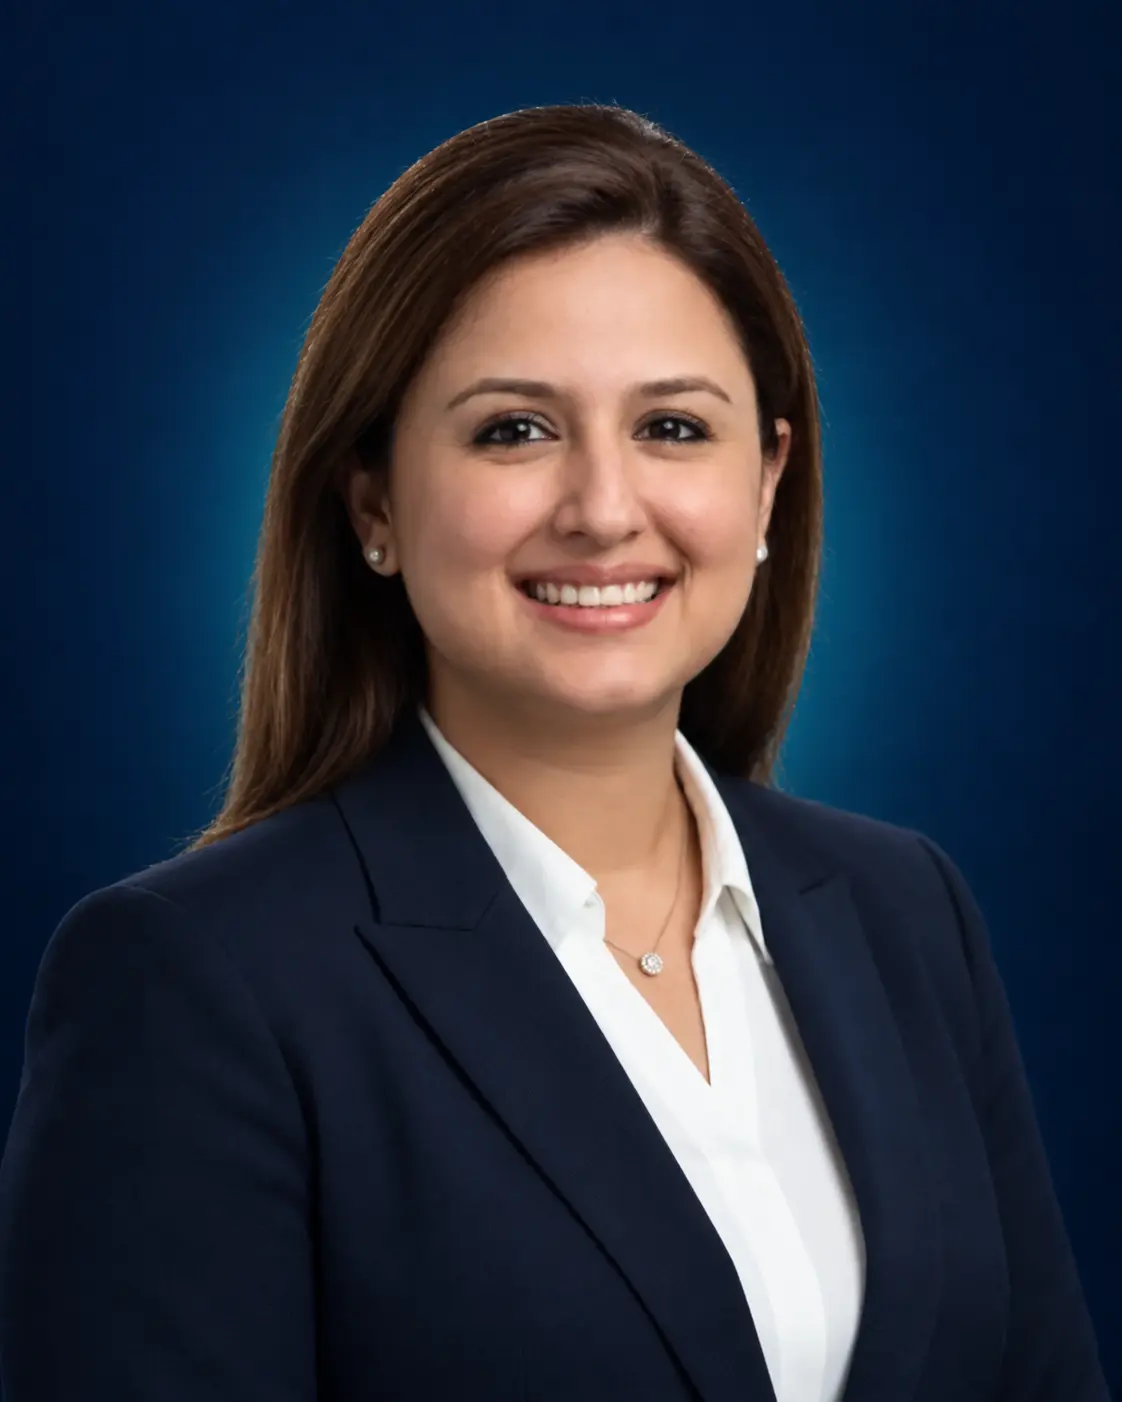
Director at Dastify Solutions | Leading Compliance and Billing Operations
With strong expertise in healthcare regulatory compliance, Anum Naveed leads Dastify's compliance oversight, ensuring alignment with HIPAA, CMS regulations, and evolving healthcare laws. She drives internal audits, risk management, and policy governance to safeguard operational integrity and data protection across all revenue cycle functions.
Proven track record
As Director of Compliance at Dastify Solutions, Anum Naveed leads all internal and external audit programs, policy governance, and regulatory accuracy initiatives. Her career spans multiple U.S. healthcare organizations where she implemented compliance infrastructures aligned with HIPAA Privacy and Security Rules, CMS Program Integrity mandates, and OIG audit protocols. Drawing on experience across revenue cycle management, medical coding, and payer relations, she specialises in translating legal and regulatory language into actionable operational controls.
Before joining Dastify Solutions, Anum collaborated with several RCM companies in the United States, developing documentation guidelines, conducting compliance risk assessments, and training staff on audit readiness. At Dastify, she now oversees the intersection of compliance, data governance, and revenue integrity — reviewing every clinical and billing process for accuracy, transparency, and ethical standards. Her oversight ensures that all content published or reviewed by Dastify reflects current U.S. healthcare law, payer policies, and CMS updates.
Oversight of compliance programs aligned with HIPAA, CMS regulations, OIG guidance, and federal/state healthcare laws to safeguard organizational integrity.
Design and execution of internal compliance audits, risk scoring frameworks, corrective action planning, and documentation governance controls.
Monitoring of CMS transmittals, final rules, and payer bulletins to ensure operational policies reflect current regulatory requirements.
Implementation of HIPAA privacy and security controls, breach prevention protocols, workforce training, and documentation standards.
Governance of AI-driven RCM tools to ensure ethical usage, documentation transparency, audit traceability, and regulatory alignment.
Development of compliance training modules and internal policy guidance to ensure company-wide adherence to healthcare regulations.
Formal training in HIPAA Privacy Rule, Security Rule, and Breach Notification standards.
Ongoing professional education in CMS program integrity, documentation standards, and audit defence strategies.